
Last chance! 50% off DataCamp Premium
Sale ends in
Buy Now
Security is paramount in enterprise storage systems. There are various ways to securely access Azure Blob Storage, such as SAS tokens, access keys, and enterprise accounts.
In production environments, you restrict access to files and data stored in Blob Storage. You generally don’t want it to be publicly accessible. Shared Access Signatures (SAS) offer a secure method of managing access to your Blob Storage data.
SAS works via tokens, which are appended to the URL of the resource you want to share. The token includes information on the type of permission (read, write, delete, etc.), the validity of the token, and the protocols (HTTP and/or HTTPS) allowed to access the resource.
For example, if a blob’s URL is:
https://my_account.blob.core.windows.net/my_container/my_file
After appending the token, it looks like:
https://my_account.blob.core.windows.net/my_container/my_file?sp=r&st=TIME&OTHER_PARAMETERS
The steps below show how to use the Azure portal to generate a SAS token for a specific container.
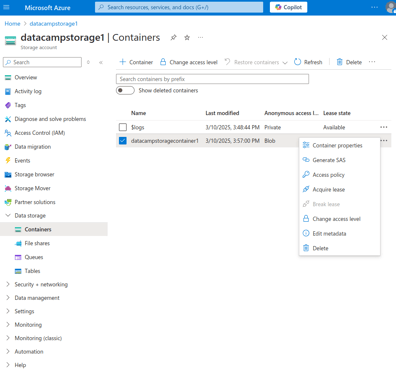
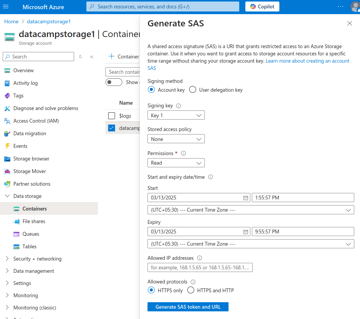
In the Generate SAS window:
You can now access a private blob using the generated token and URL. When you try to access a private blob without the proper access tokens, you get an XML error that says, “The specified resource does not exist.”
Microsoft Entra ID manages user identities and roles in one place and allows granular access to Azure resources. In addition to SAS tokens and keys, it provides another (more secure) option for managing access to Azure Blob Storage entities. You can grant specific permissions to individual users or groups by assigning them appropriate roles. This is called Role-Based Access Control (RBAC).
RBAC facilitates fine-grained access control by having roles such as Owner, Contributor, and Reader. You can define these permissions at various levels, such as the entire Storage account or individual containers.
For example, for a particular storage account, you can assign a user the role of Storage Blob Data Reader. That user will then be able to read only the blobs in that account but not do anything else (like write or list all the blobs).
You can integrate Azure Blob Storage with enterprise authentication systems, using Entra IDs to authenticate users. Enterprise Azure users and applications already have (or can get) Entra IDs, making it easier to manage authentication centrally using existing enterprise credentials.
Note that Microsoft Entra ID is the new name for Azure Active Directory (AD).
In the next section, I will show you how to assign users roles and manage access to Blob Storage entities.
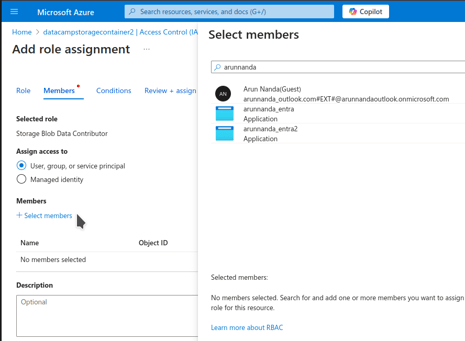
I will show you how to configure access by assigning roles for a Storage Container. The process for Storage Accounts is similar.
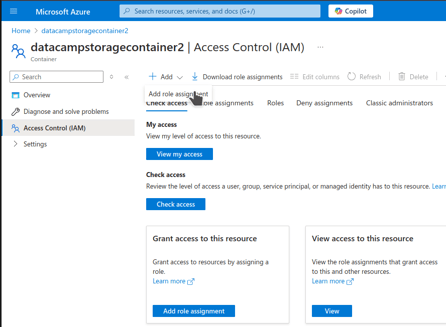
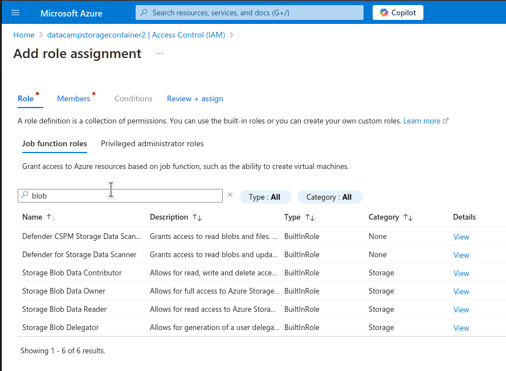
You can choose from three types of roles for Blob Storage:
Note that roles are inherited. For example, if you assign a user the “Owner” role for a Storage Account, that user also becomes the owner of the Containers in that account.
We’ve reviewed the basics of Azure Blob Storage, but once you want to take it to the next level, here are some strategies to consider.
Frequently accessed data should be stored in fast-access storage tiers like Hot. Rarely accessed data can be stored in slow but economical storage tiers, like Archive storage.
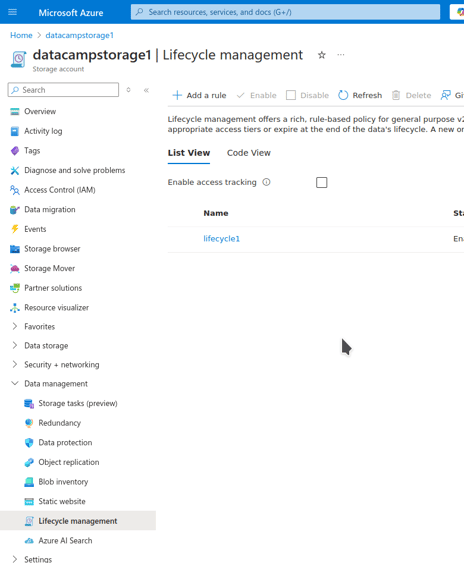
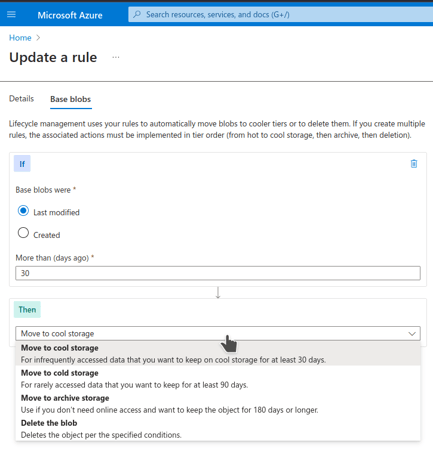
The challenge is dynamically figuring out which blobs are no longer frequently accessed and can be moved to cheaper storage. To do this automatically, Azure comes with a Lifecycle management feature. This feature lets you dynamically move blobs to cheaper storage when they are no longer actively modified.
Lifecycle management is implemented at the Storage Account level. The steps below show how to activate and use it to add a rule to move blobs from Hot to Cool storage after 30 days of inactivity:
In any storage system, it is essential to recover from user errors and unintended actions. Versioning and soft delete are the two ways Azure Blob Storage uses to help you undo mistakes.
It is useful to be able to restore the previous versions of a file if you accidentally save the wrong changes. Blob versioning allows you to automatically retain older versions when you modify a blob. To enable versioning:
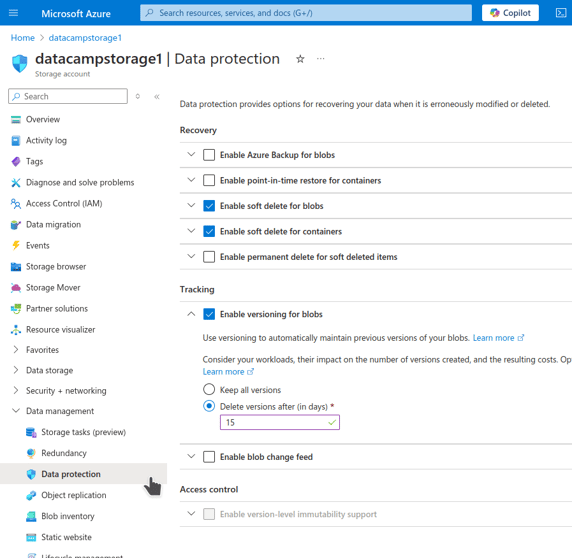
Versioning is now enabled on your storage account!
We have all accidentally deleted the wrong data. It is useful to be able to recover the lost data when this happens.
Blob soft delete is a feature that retains the deleted data for a specified number of days. During this retention period, you can restore the soft-deleted entity. After the retention period, the data is permanently deleted. This protects data from accidental deletion and overwriting.
To activate and use soft-delete:
You have now activated soft-delete on your storage account!
By default, Azure employs AES-256 symmetric encryption at rest to keep data secure. An attacker with physical access to the hard drive on which the data is stored cannot decrypt the data without the encryption keys. Many organizations need this feature for security and compliance with privacy regulations.
By default, the user does not need to handle the additional workload of maintaining encryption keys. Azure takes care of it under the hood. However, you can choose to use the key vault and provide your keys for added security:
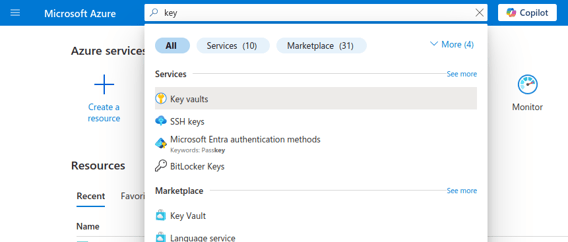
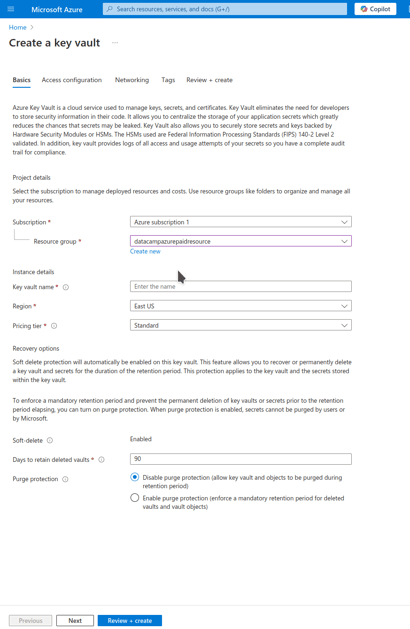
Creating the new key vault takes a while and then directs you to its page.
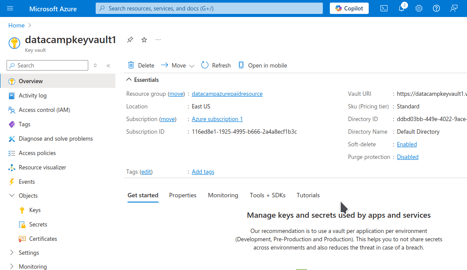
After creating the key vault, you can now add your keys and secrets:
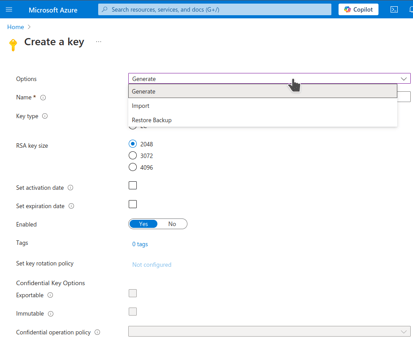
You have now added a key to your keyvault.
The safer you need your data to be (from technical or natural calamities), the more redundancy you build into your storage system. Redundancy involves replicating the same data across multiple devices and/or locations and comes at a cost. You can choose from various levels of redundancy:
Cloud storage, for all its benefits, can become expensive if costs are not managed properly. In this section, I will give an overview of how to optimize and manage costs for Azure Blob Storage.
Azure Storage has various tiers of pricing depending on the options and additional services offered:
Based on the discussion above, I recommend a few best practices to prevent cloud storage costs from spiraling out of control.
Although Azure Storage is a widely used product, errors sometimes occur.
Network issues and permission errors are among the most common types of problems. Slow connections and misconfigured proxies frequently lead to network errors, which can be best resolved by checking your connection and configuration.
It is also common to get errors when trying to upload large files. A momentary loss in network connectivity can lead to the upload being stalled. To address such issues, check Azure’s retry policies and configure them as needed. Another pragmatic solution is to break up large uploads into smaller chunks. Upload each chunk separately using the Put Block operation.
Permission errors are caused when your access keys or tokens, or Entra ID, are not authorized to perform your desired operation (e.g., read or write data) to the storage container or account. It is possible your keys have been refreshed, or your token has expired. The container manager can help you get the correct access rights.
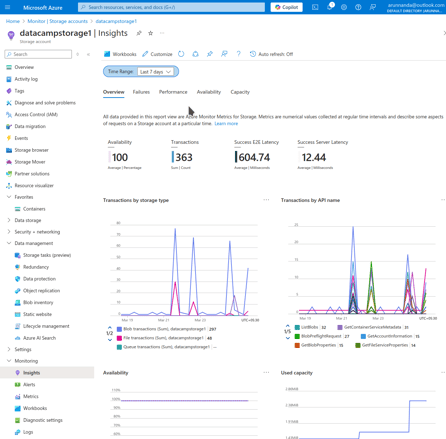
Azure includes various tools to monitor the performance of Azure Storage. We will cover two of the most common choices:
Azure Storage comes with an integrated monitoring tool. To access it:
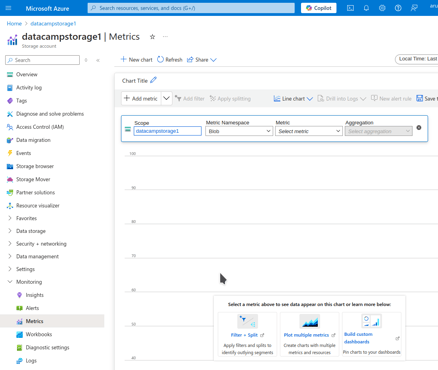
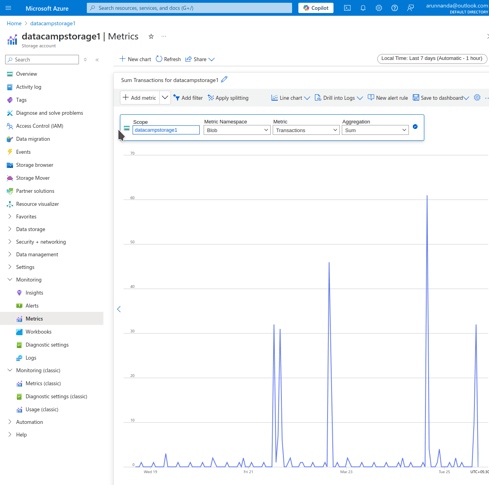
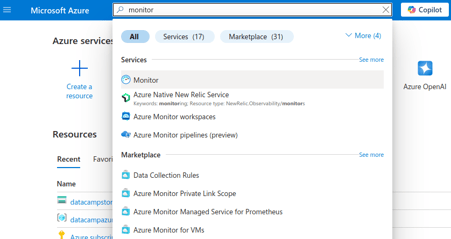
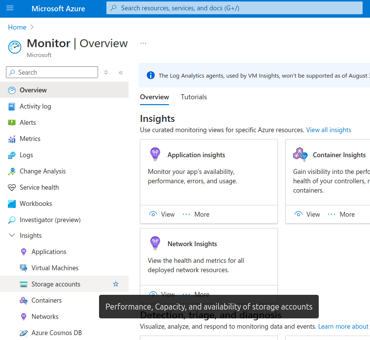
Azure Monitor is a high-level tool that you can use to monitor various Azure resources. To access Azure Monitor:
Cloud storage is an integral part of modern software. In this article, we discussed how to get started with Azure Blob Storage and how to use it to upload and download blobs. We also covered many practical aspects of Blob Storage, such as managing access rights and monitoring usage to control costs.
Microsoft’s Azure and Amazon’s AWS offer many overlapping services. To decide which better suits your individual needs, go through our AWS vs. Azure comparison. Finally, if you have an upcoming interview involving Azure services, we have a set of relevant interview questions for you!

Arun is a former startup founder who enjoys building new things. He is currently exploring the technical and mathematical foundations of Artificial Intelligence. He loves sharing what he has learned, so he writes about it.
In addition to DataCamp, you can read his publications on Medium, Airbyte, and Vultr.

บทแนะนำ
 Anneleen Rummens• 11 นาที

บทแนะนำ
 Arun Nanda• 15 นาที

บทแนะนำ
 Emmanuel Akor• 15 นาที
Learn more about Azure with these courses!
คอร์ส
เรียนรู้พลังของ Microsoft Azure และซอฟต์แวร์คลาวด์คอมพิวติ้งเพื่อช่วยพัฒนาทักษะวิศวกรรมข้อมูลของคุณ
คอร์ส
หลักสูตรนี้เจาะลึกโครงสร้างหลักของ Azure โดยครอบคลุมหัวข้ออย่างคอนเทนเนอร์ เครื่องเสมือน และอื่นๆ อีกมากมาย
แทร็ก
เตรียมความพร้อมสำหรับการรับรอง Azure Fundamentals ของ Microsoft (AZ-900) ด้วยการเรียนรู้พื้นฐานของ Azure: การประมวลผล, การจัดเก็บข้อมูล และเครือข่าย


Cloud storage can feel like a black box until you actually dive in and use it—and Azure Blob Storage is a great place to start. Whether you’re dealing with images, text files, videos, or backups, Blob Storage gives you a scalable and secure way to store unstructured data in the cloud.
In this tutorial, I’ll walk you through the essentials of Azure Blob Storage—what it is, why it matters, and how to get started. We’ll go hands-on with uploading and downloading data, setting permissions, and managing lifecycle policies to keep your storage lean and efficient. Whether you're exploring Azure for the first time or adding blob storage to your cloud toolkit, this guide will help you hit the ground running.
What is Azure Blob Storage?
“Blob” stands for Binary Large Object—a term used to describe storage for unstructured data like text, images, and video. Azure Blob Storage is Microsoft Azure’s solution for storing these blobs in the cloud.
It offers flexible storage—you only pay based on your usage. Depending on the access speed you need for your data, you can choose from various storage tiers (hot, cool, and archive). Being cloud-based, it is scalable, secure, and easy to manage. As an Azure service, it can be integrated with other Azure services like Azure Backup, Azure Synapse, Azure CDN, Azure ML, and more.
If you're new to Azure’s broader ecosystem, our course on Understanding Microsoft Azure Architecture and Services offers a structured introduction.
Setting Up Azure Blob Storage
Now, let’s get hands-on and start working with Azure Blob Storage! For this tutorial, I assume you already have an Azure account - either a trial account with free credits or a regular paid account.
Creating a storage account
To start with, we create a Storage account on the Azure portal:
datacampstorage1.The next page confirms that the storage account is deployed. Select the Go to resource button to view the details of your new storage account and take further action.
You have now created a new storage account!
Configuring blob containers
Azure Blob Storage organizes data into containers. Each container can store many blobs, similar to a directory in a file system. Blobs in a container can be of various file types, like PDFs, videos, and more. Use containers to organize your data based on regions, projects, etc.
To create a container:
datacampstoragecontainer1.The Containers page now shows the new container:
Uploading and Managing Blobs in Azure Blob Storage
There are three main ways to upload a blob to the storage container: the Azure portal, the Command Line Interface (CLI), and the Storage Explorer application. In this section, I will explain how to use each method to upload a file to Blob Storage.
Using the Azure portal
To upload a file using the Azure portal:
As an alternative to the steps described above, you can also select an individual container from the Containers page and then select the Upload button at the top.
Using the Azure CLI
To upload a file to Blob Storage using the CLI:
foobar.txtto test:Ctrl + S, and exit the Nano editor usingCtrl + X.Qto exit the output ofless.We now need to upload this file to Blob Storage:
In the command above, the name of the storage account is
datacampstorage1and the container's name isdatacampstoragecontainer1. If you used different names, substitute them as appropriate.After it uploads the file successfully, you should see a message resembling the output below:
If you're using the command line, keep our handy Azure CLI cheat sheet nearby for quick reference on essential commands.
Using Storage Explorer
You can also use Azure’s Storage Explorer application to upload blobs to Blob Storage. To upload files to Azure Blob Storage:
Managing blobs
After uploading files to blob storage, I will show you how to list the blobs in a container and how to download blobs.
Listing blobs
We will use the Azure portal and the CLI to view a list of the blobs in a container.
Azure portal
On the Azure portal, on the Containers page:
Azure CLI
On the Azure CLI, use the following command:
As before, substitute the correct values for your storage account and container names. The output resembles the example below:
Downloading blobs
As before, you can download blobs from either the Azure portal or the CLI.
Azure portal
To download a blob via the Azure portal:
Azure CLI
To download a blob using the Azure CLI, use the command below:
Remember to use the correct values for the parameters in the above command.
The blob gets downloaded to the Azure remote filesystem. For example, to view the contents of the
/tmpdirectory used above, use thelscommand in the Azure CLI:Note that the Azure CLI has neither access to nor knowledge of your local machine.
For a deeper look into managing CI/CD pipelines in the Azure ecosystem, check out our Azure DevOps tutorial.
Organizing blobs with prefixes and virtual directories
Azure Blob Storage is organized as a flat file system. There is no directory or folder structure. All blobs are stored as individual files within containers.
In practice, many applications need to store data in a directory structure. For example, a CCTV monitoring system might need to store each day’s videos in separate folders. To achieve this effect, you can mimic a directory system with slash-based prefixes in the filenames.
If you have a parent directory,
month1with two subdirectories,day1andday2, each with an image file namedimage1.jpg, you would list their paths as:month1/day1/image1.jpgmonth1/day2/image1.jpgAzure Blob Storage allows you to use these paths (including parent directory names and slashes) as the blob's filenames.
day1andday2are not directory names but part of the filenames of the respective blobs. Your application can benefit from organizing files into a directory structure using this pseudo directory structure.For structured data storage needs alongside blobs, you might also explore our Azure SQL Database guide.