

Managing Storage Resources
In this section, I will show you how to manage storage resources. We will cover how to rename, delete, and refresh files and containers and monitor user activity.
Renaming and deleting files/containers
You can use Storage Explorer to perform management tasks directly, such as deleting and renaming containers and files.
To delete a container:
- Select the container in the sidebar.
- Right-click to show the context menu.
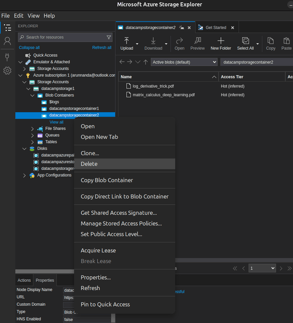
- Select the Delete option.
- Select Yes in the confirmation window.
To rename a container:
- Clone the container with the appropriate name:
- Right-click the container’s name in the sidebar to show the context menu.
- Select the Clone option.
- Enter the appropriate name.
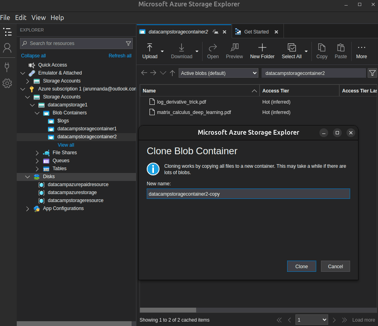
- Delete the old container, as shown earlier.
Note that it is not possible to directly rename a container, either using Storage Explorer or the portal.
Similarly, to rename a file, clone it using a new name:
- Select the file in the Explorer window.
- Right-click to show the context menu.
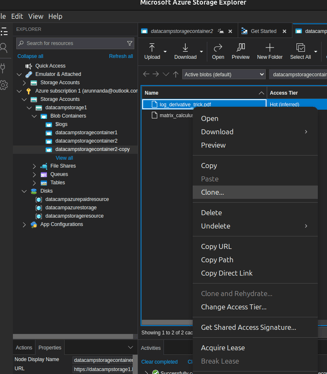
- Select Clone.
- Enter the appropriate new name.
- Delete the old file.
You can delete a file in two ways:
- Select Delete from the context menu (shown above).
- Select the Delete button in the top bar.
For those integrating storage with deployment pipelines, check out our Azure DevOps Tutorial to learn how to build, test, and deploy efficiently.
Monitoring activity and logs
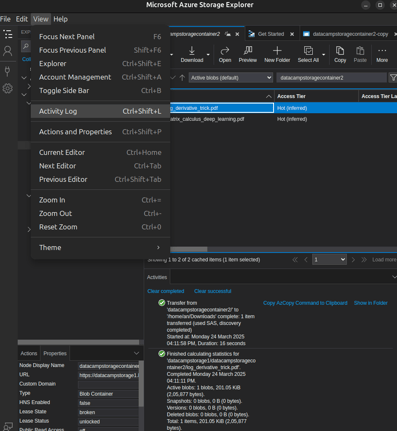
The Activity Log feature shows the activity history (such as uploads, downloads, changes, deletions, etc.) of the selected storage entity. The activity log is shown in the bottom panel. To show the log for a particular file:
- Select the file in the Explorer window
- From the menubar, select View > Activity Log
Refreshing and synchronizing data
In many cases, various people access the same container or resource simultaneously. Accessing the latest version of the files is essential to avoid confusion and stay updated with the latest changes and data. To do this:
- Select the container whose contents you want to sync to the latest version.
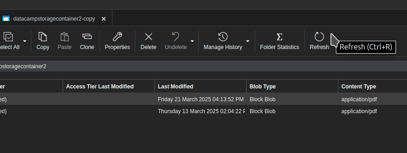
- Use the Refresh button in the top bar to sync Azure Storage Explorer's contents with the latest data from the server.
Troubleshooting Common Issues
Even though it is a widely used and regularly updated product, you can still run into issues while using Azure Storage Explorer. Let’s review common issues you can encounter and how to fix them in this section.
Resolving connection issues
Several common issues can prevent you from accessing Azure Storage resources through Storage Explorer:
- Incorrect credentials Mismatched usernames and passwords, expired access keys, or invalid SAS URLs can block access. These errors are especially common when managing multiple credentials across different resources. Having a reliable system in place is crucial to track and update your credentials.
- Network-related problems Network configurations like proxies and VPNs can interfere with access. Additionally, some storage resources use IP whitelists, which can cause trouble if you're on a dynamic IP address (common with most modern ISPs).
- Expired browser cookies Storage Explorer sometimes relies on your browser's cookies for authentication. If you suddenly can’t access an account that used to work, try the following:
- Clear your browser’s temporary files and cookies.
- Close and reopen Storage Explorer.
- Attempt logging in again.
Permissions and access control problems
Wrongly configured access methods are a common source of errors. If users are not careful, many security features also end up catching legitimate users.
- The SAS access token (and URL) might have expired. In such scenarios:
- It is necessary to get new keys periodically from the owner or manager of the resource
- It might be helpful to generate special keys with longer expiration for users who need long-term access to the data.
- Entra-based RBAC solutions are more robust than using keys.
- The access token does not have the right permissions.
- If this happens, the resource’s owner or manager must generate a set of tokens with the necessary permissions.
- As before, using Entra and RBAC gives a smoother experience and is a more secure long-term solution.
- The keys might have been regenerated.
- In such cases, the user needs to get the updated keys from the owner or manager.
- The Entra ID might now have the right authorization.
- The owner or manager of the resource can apply the right RBAC credentials to your Entra ID.
Best Practices for Using Azure Storage Explorer
In this section, I share some of my best practices to make the most of Azure Storage Explorer.
Secure authentication and access control
Managing access to Azure Storage resources securely is critical. Here's a breakdown of common methods and their pros and cons:
Shared Access Signatures (SAS keys and URLs)
While convenient, SAS keys are not ideal for robust access control due to several limitations:
- Difficult to track which keys were issued to which users.
- Hard to manage expiration dates and specific access rights.
- Keys must often be shared via insecure channels (e.g., email), making them vulnerable to man-in-the-middle attacks.
- Users can easily confuse different keys, leading to mistakes.
Despite these issues, SAS keys are often preferred for short-term use because they’re easy to generate and distribute.
Role-Based Access Control (RBAC) with Microsoft Entra
For longer-term access and more secure management, RBAC is the recommended approach:
- Microsoft Entra enables fine-grained access control.
- Storage administrators can centrally assign specific roles and permissions to users.
- Reduces the need to distribute or manage multiple keys.Enhances security by tying access to user identities instead of shared credentials.
Organizing storage accounts
Proper organization of your Azure Storage resources helps you manage complexity and maintain clarity across environments. Here are some best practices:
- Use separate storage accounts for different environments. For example, keep development, testing, and production files in distinct accounts. This separation reduces the risk of cross-environment interference and simplifies access control.
- Group storage accounts by logical categories. Organize accounts based on:
- Projects.
- Geographic regions.
- Application components.
- Apply meaningful naming conventions. A prefix-based naming system improves clarity when managing hundreds of containers and accounts. Include context such as environment, purpose, or region. Example:
Prod-Media-Asiaas a container name → stores media files for the production app in the Asia region.Prod-Mediaas a storage account name → hosts large media files used in production apps.
This structure improves navigation and aligns storage configurations with each account’s intended use.
Regular backup and monitoring
Ensuring your Azure Storage setup is reliable and cost-efficient requires regular backups and active monitoring. Here’s how to stay on top of both:
- Back up your data regularly
- Just like any other system, cloud storage needs a robust backup strategy.
- Store backups in different geographic regions to protect critical files from regional outages.
- In some cases, consider on-premises backups as an additional layer of redundancy.
- Monitor usage and costs
- In Azure, you’re charged for:
- Storage space
- Data egress (downloads)
- Access frequency (varies by storage tier: hot, cool, archive)
- To keep expenses manageable, it’s important to monitor:
- Access patterns – Identify files that are frequently accessed.
- Storage tier usage – Ensure files are in the appropriate tier based on how often they’re accessed.
- Optimize performance and user experience
- Use a Content Delivery Network (CDN) in front of read-heavy files (e.g., large video files) to reduce latency and egress costs.
- If most traffic comes from a particular region, consider replicating storage in that region for faster access.
- Track and analyze errors
- Inaccessible files can lead to lost business or poor user experiences.
- Regularly review error logs to identify and troubleshoot access issues.
- Tools like Storage Explorer’s Access Logs can help you monitor:
- File access patterns
- Usage trends
- Authentication or access errors
Conclusion
Azure Storage Explorer simplifies how you interact with your Azure Storage resources—offering a clean, intuitive interface to manage blobs, files, queues, and tables without diving into the full Azure portal. In this tutorial, you learned how to install the application, connect to your storage accounts, and securely manage your data with ease.
Preparing for an Azure-related job interview? Don’t miss these 30 Azure Interview Questions that range from basic to advanced.

Arun is a former startup founder who enjoys building new things. He is currently exploring the technical and mathematical foundations of Artificial Intelligence. He loves sharing what he has learned, so he writes about it.
In addition to DataCamp, you can read his publications on Medium, Airbyte, and Vultr.


If you’ve ever found managing cloud storage through the Azure portal a bit clunky or overwhelming, you’re not alone. That’s where Azure Storage Explorer comes in—a user-friendly desktop application that lets you interact with your Azure Storage resources without needing to navigate the full Azure interface.
In this tutorial, I’ll walk you through Microsoft’s Azure Storage Explorer: how to set it up, connect to your storage accounts, and start managing your blobs, queues, tables, and files with ease.
What is Azure Storage Explorer?
Azure Storage Explorer is a free cross-platform tool by Microsoft. It allows you to access data (like blobs, tables, queues, and files) stored in Azure Storage and provides limited management features to manage the stored data. You can upload, explore, download, and clone data entities.
Being a locally installed application, it provides a simple and familiar user interface without depending on web browsers or CLIs.
To better grasp how Storage Explorer fits into the broader cloud ecosystem, explore the Understanding Microsoft Azure Architecture and Services course.
Installing Azure Storage Explorer
In this section, I will show you how to set up Azure Storage Explorer and start using the application.
Downloading and installing
To download and install Storage Explorer:
.exefile..tarfile.In this tutorial, I will install the app via the Linux Snap Store. All the screenshots are based on Ubuntu Linux in dark mode. Since software packages and webpages are frequently updated, what you see may not exactly match my screenshots.
Launching Azure Storage Explorer
Launch the Storage Explorer like any other app on your operating system:
The user interface is similar to that of other Microsoft applications like VSCode. You have a main window that can contain tabs. The left menu is collapsible and contains four options:
Select each option in the left menu to expose the sidebar corresponding to that option. We will use these options and cover them in greater detail in later sections.
At the bottom, you have a panel that shows a log of various actions and their status.
Connecting to Azure Storage Accounts
After launching Storage Explorer, we will connect it to your Azure Storage account.
Signing in with an Azure Account
You can use your Azure account to connect Storage Explorer to Azure Storage:
Having logged in to Azure, we will see (in the next section) how to connect to different resources from your Azure account.
Connecting to Different Types of Azure Storage
Using Storage Explorer, you can connect to various types of storage resources, such as Blobs, Files, Queues, and Tables. Let’s explore how in this section.
Connect to Blob Storage
To connect to Blob Storage:
If the Entra ID linked to the Azure account you used to sign in (above) is authorized to access the Blob Container, it connects successfully. You can then open it in Storage Explorer:
Other types of storage resources
The process of attaching other resources, such as files, queues, and tables, is similar to attaching a storage account, as shown above.
Navigating and Managing Azure Storage Resources
After connecting Storage Explorer to Azure Storage, we will learn how to navigate and manage storage resources using the application.
Browsing blob storage
Browsing containers and blobs in Storage Explorer is similar to using the file explorer on the computer. After connecting to a storage account (as explained earlier):
Uploading files to Azure Blob Storage
To upload files to Azure Blob Storage:
The bottom panel shows the selected file's uploading status. When the upload completes, the Explorer tab automatically updates to show the newly uploaded file.
Managing Azure files and shared folders
You can also use Azure Storage Explorer to manage file shares and directories. You can upload entire folders from your local computer or directly create a folder within Azure Storage.
To upload a folder:
To create a new folder (without uploading):
The process of uploading a file is similar to uploading a folder:
To delete a file:
Alternatively, right-click the file name and select Delete from the context menu options.
Working with Advanced Features
Having covered the basics, I will show how to work with SAS tokens and access keys.
Generating and using Shared Access Signatures (SAS)
To access storage entities (like blobs, queues, etc.) using SAS, you need a connection string (URL) that contains the SAS token. You get the connection string from the Azure portal:
You can now connect to your Azure Storage account using this SAS token. To attach a Storage Account within Storage Explorer:
To connect using the SAS token:
After connecting, you can access the contents in Storage Explorer:
Managing access keys and secrets
In addition to the methods discussed above, you can use your Azure account’s access keys to connect Storage Explorer to Azure Storage. Share the account name and key with anyone, and they can securely connect to your Storage resources without relying on Microsoft Entra ID.
If you choose to connect using the account name and access key, you will need the key from your Azure account. To get the key:
To connect using the
After connecting, you can access the contents in Storage Explorer:
You will find the contents of the storage account in the sidebar. Notice the suffix “(Key)” next to the Storage account name. The contents are organized as an expandable tree structure. Selecting each item in the tree will show its contents.
Using Microsoft Entra (formerly Azure Active Directory, AAD) authentication
The above methods (SAS tokens and access keys) require you (as the owner of the storage entity) to use a URL or a key to access the data. While convenient, this method is not the safest. For example, keys and tokens can be intercepted during the sharing process. Using Microsoft Entra (formerly Azure Active Directory) is a better option.
In corporate environments integrated with Microsoft Entra, you can use your Microsoft Entra account to access and manage data stored in Azure Storage. Note that Microsoft Entra can be used only with blob, queue, and table data.
When using Entra ID, you can also take advantage of Role-Based Access Control (RBAC). RBAC allows you to manage access to Azure resources by assigning permissions to users, groups, and applications based on their roles. The Azure Blob Storage tutorial describes in greater detail how to set permissions for storage entities using the Azure portal.
After you sign in to Storage Explorer using your Azure account, you can access Storage entities your Entra ID is authorized to access. Earlier in this article, you signed in to Blob Storage using OAuth. That method authenticated you based on the Entra ID tied to the account you used to log in via OAuth. Notice the suffix “OAuth” is beside the name of the Blob Container in the sidebar.
If you're also working with Azure SQL, our step-by-step guide helps you manage database storage.